#12 · Security and governance
What controls exist when AI agents access client systems?
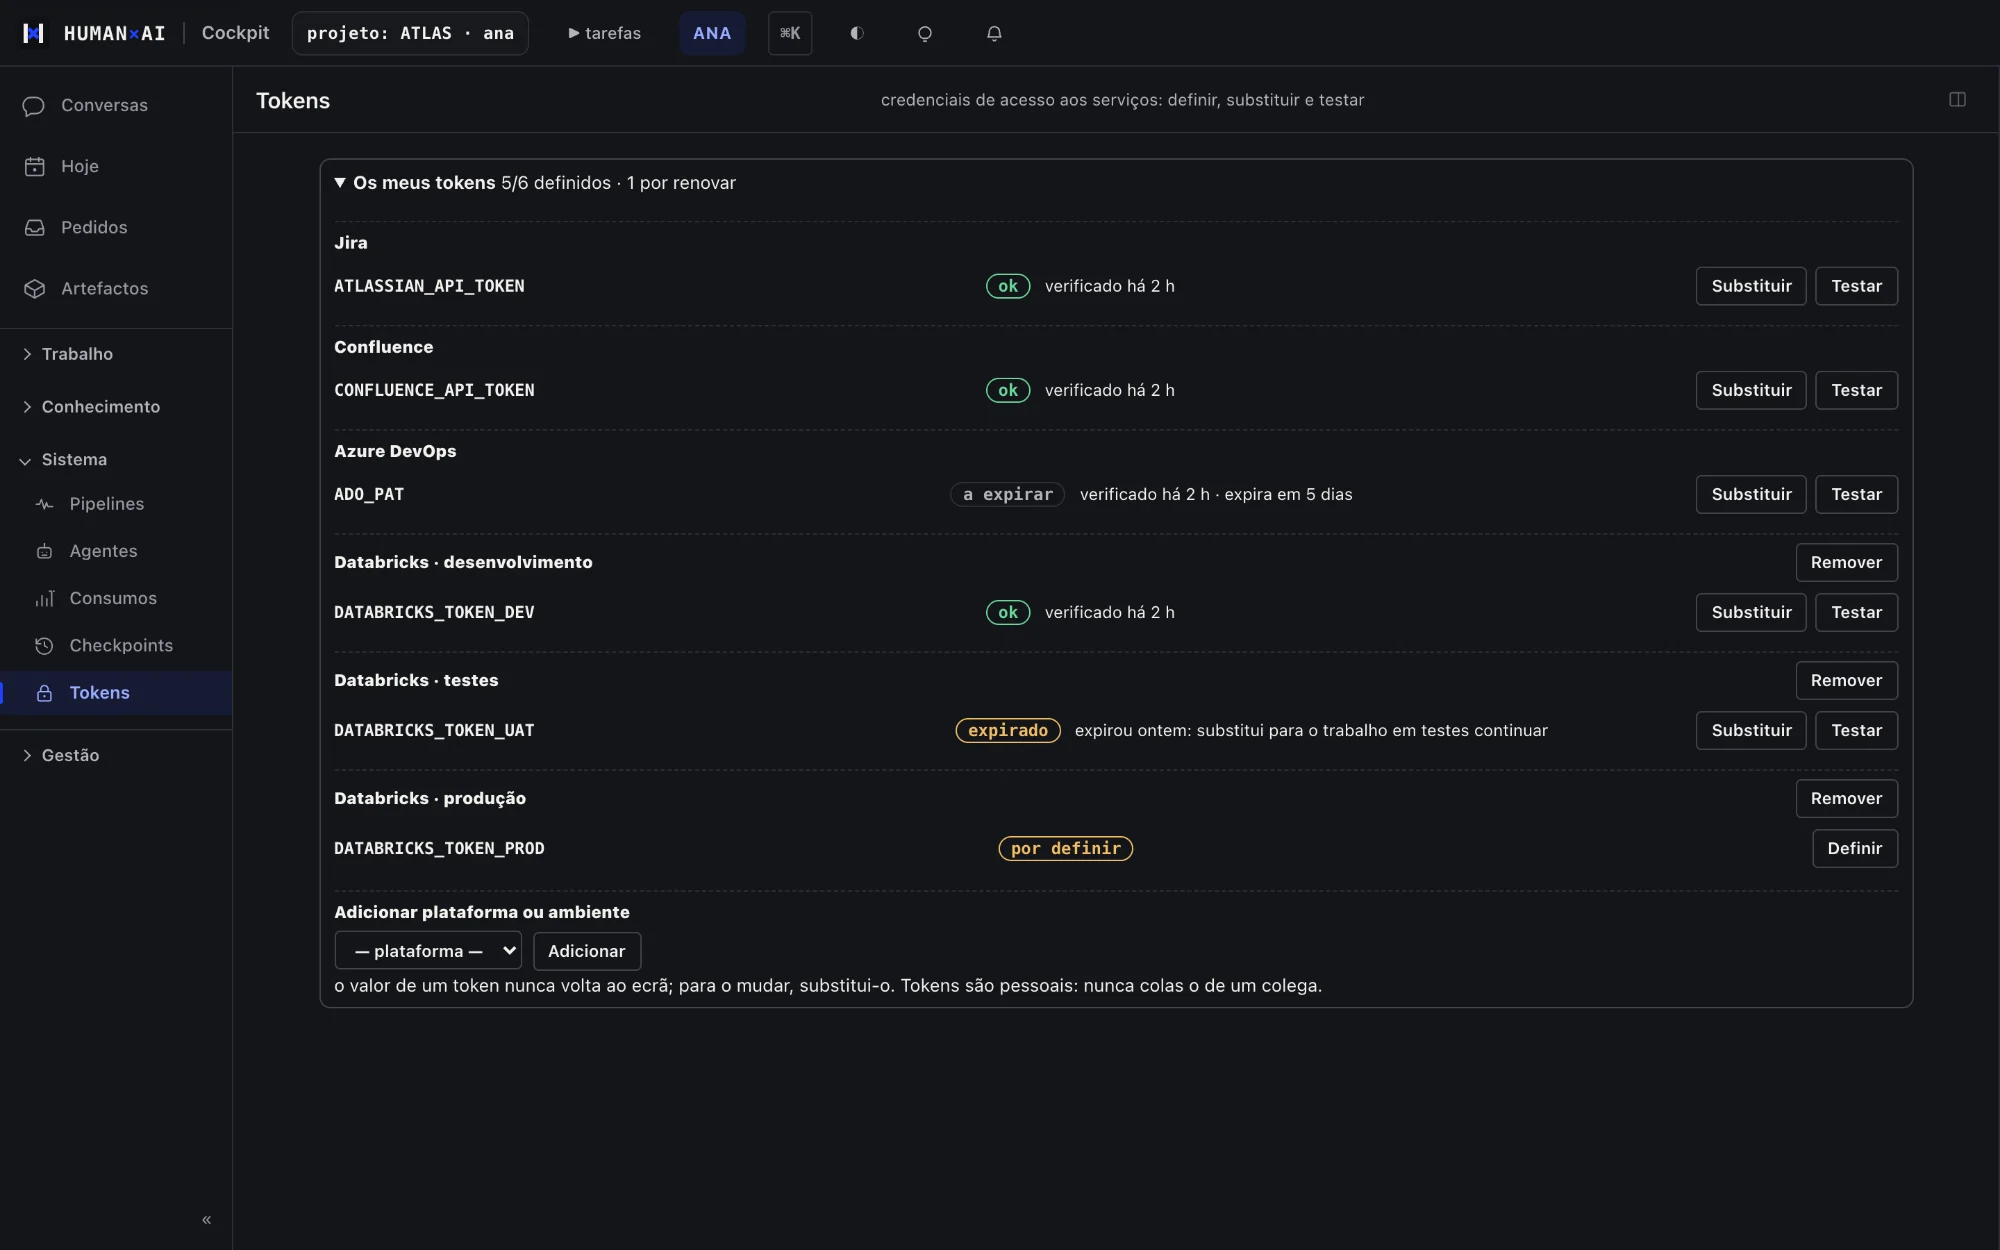
In the HumanAI platform everyone has an isolated environment and personal credentials that are never shared. Secrets are blocked before they reach a file, and as a rule client data rows are not copied into documents or the team's knowledge.
The problem
Agents with access to client systems need more control, not less.
How it works
- Every agent action goes through the platform's guards.
- Anything sensitive asks for a person.
- Everything is recorded for audit.
What it includes
- A personal, isolated environment that keeps working with the laptop closed
- Personal credentials, never shared, with automatic detection of sharing
- A secrets guard that blocks keys and passwords before they reach a file
- Client data rows kept out of documents and team knowledge: only metadata and aggregates
- Separation between projects, checked before every distribution
- Human authorship: work goes out signed by the person
- Second factor on platform approvals and an audit trail of actions
- Content-free notifications: the phone alert carries no project data
What sets it apart
These controls run on every agent action, without relying on anyone to remember them.
Questions
Who sees my credentials?
Only the person sets and uses them; they are not shared.
Where is the list of sub-processors?
On the Sub-processors and integrations page.